
Your AI agents have access. Do you know what they can do?
Agentic AI and workload identities are multiplying across enterprise environments without governance controls. Modern 42 provides dashboards and observability across your application identity estate, quantifies the risk, and builds the governance frameworks to manage it.
Your fastest growing attack surface has no controls
Every AI agent, automation pipeline, and SaaS integration authenticates as an application identity. These identities accumulate over years of project work, proof-of-concept deployments, and vendor integrations. Permissions are granted at creation and rarely reviewed. Owners leave the organisation. Credentials expire or, worse, never expire. Most organisations have no visibility into what these identities can access, who created them, or whether they are still needed.
Agentic AI risk
With the rise of agentic AI, the problem is accelerating. Copilot agents, custom AI assistants, and autonomous workflow bots are being provisioned with broad permissions to access production data, send emails, and modify configurations. Most have no approval workflow, no expiry, and no audit trail.
Common findings
- Over-privileged applications with excessive Graph permissions
- High-privileged dormant applications with no recent sign-in activity
- AI agents with broad data access and no approval workflow
- Ownerless service principals with no accountability
- Client secrets with multi-year or no expiry
- Applications excluded from Conditional Access policies
- No inventory of what non-human identities exist
of enterprise applications will include agentic AI by 2028, up from less than 1% in 2024. Most organisations have no governance framework for these identities.
Top Strategic Technology Trends for 2025/Gartner, October 2024
Eight domains of application identity risk
Each domain is assessed using data extracted directly from your Microsoft Entra ID tenant. We quantify the risk, identify the gaps, and prioritise what to fix first.
App registrations and service principals
API permissions and OAuth consent
Legacy configurations
Agentic AI and Copilot permissions
Secret and credential management
Application lifecycle and ownership
Insecure configurations
Cross-tenant and external access

Visibility. Risk scores. A governance framework.
The assessment delivers three things: a clear picture of your current state, a quantified risk profile, and a practical framework for managing application identities into the future.
Dashboards and Observability
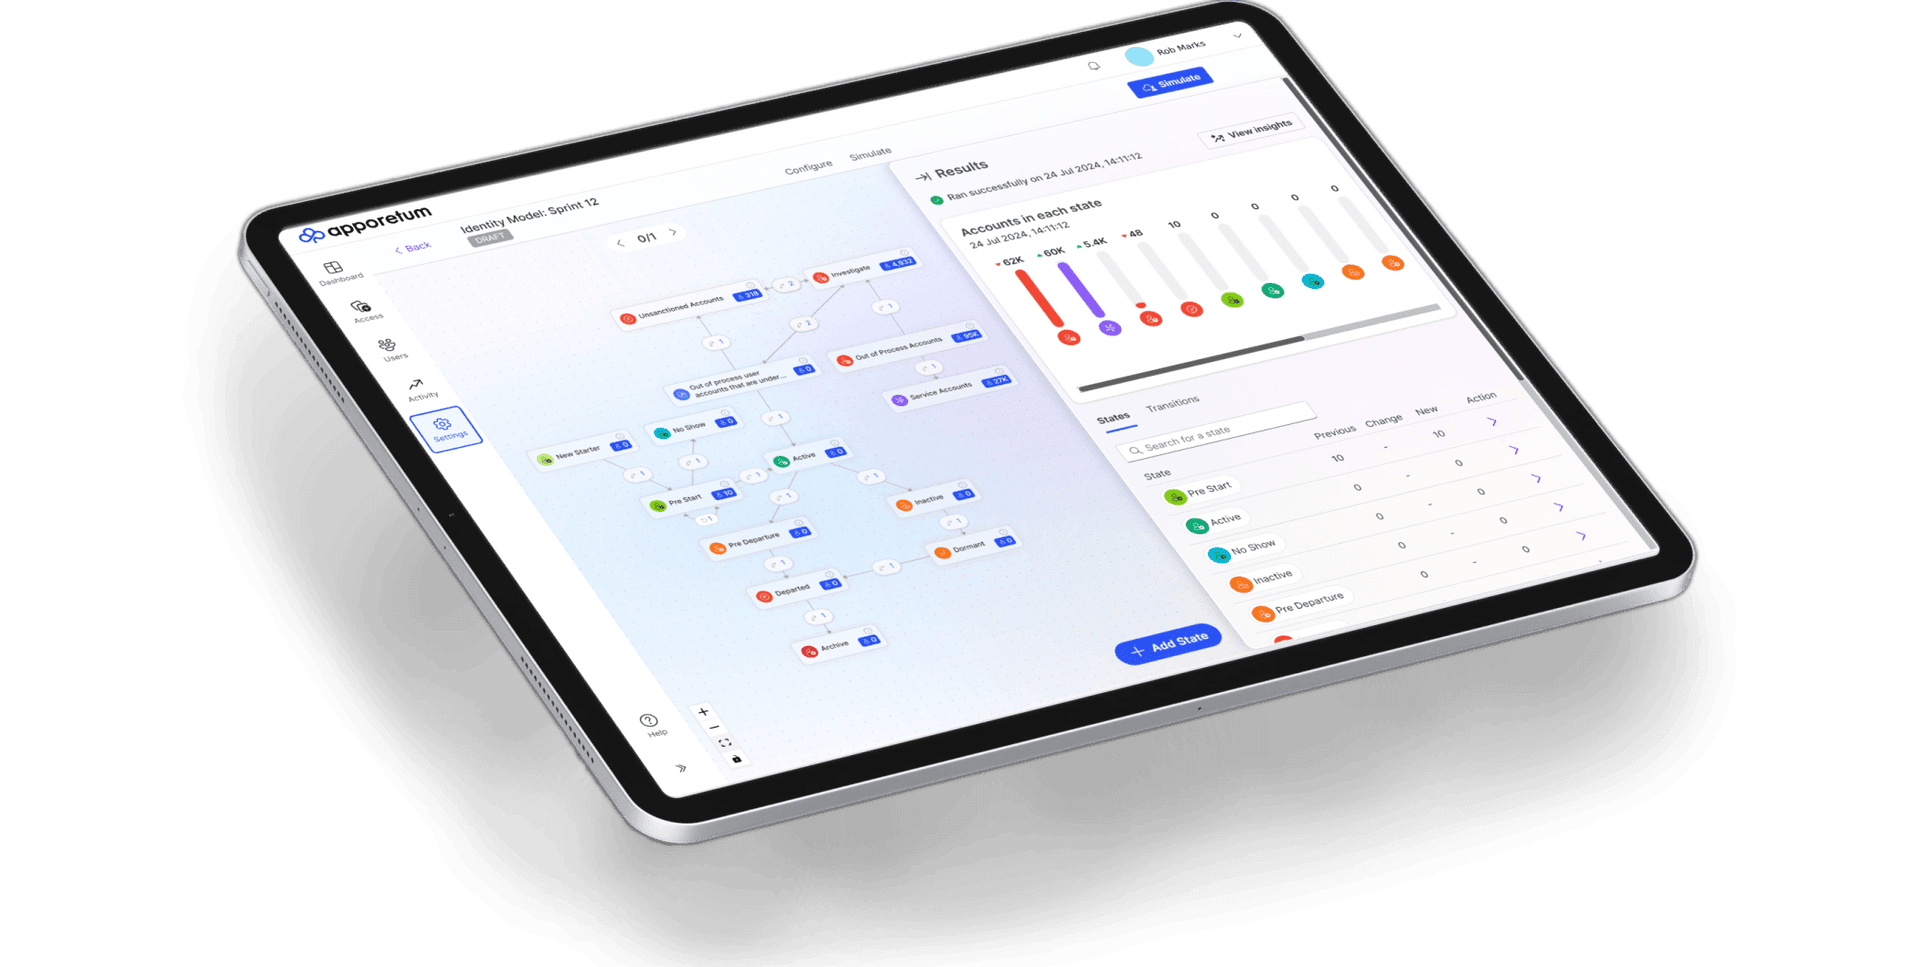
Using Apporetum, we surface every application identity in your tenant: app registrations, service principals, managed identities, and AI agents. You see what exists, who owns it, what it can access, and whether its credentials are current.
Risk quantification
We score each application identity against permission scope, credential hygiene, ownership status, and policy coverage. The result is a prioritised risk register that tells you exactly where to focus remediation effort.
Governance framework
Beyond the assessment, we build a governance framework for managing application identities into the future: approval workflows, permission standards, lifecycle policies, and review cadences tailored to your organisation and to where it sits on the application identity maturity model.
Engineering pathway
For organisations ready to operationalise governance at scale, our engineering team delivers deterministic, configuration-driven application onboarding pipelines. These enable self-service within guardrails, enforce standards automatically, and provide backup and recovery for critical application configurations.
What you receive
A structured report with findings, risk scores, and a governance framework you can implement immediately.
- Complete inventory of application identities, service principals, and managed identities
- Permission analysis with over-privilege scoring for each identity
- Agentic AI and Copilot agent mapping with governance gap analysis
- Credential hygiene report (expiry, rotation, Key Vault adoption)
- Prioritised remediation roadmap with 30/60/90-day milestones
- Application identity governance framework with approval workflows and lifecycle policies
- Executive summary suitable for board, CISO, and audit reporting
- Actionable best-practice recommendations to improve your security posture
- Single pane of glass for visibility and reporting across your application identity estate
See the work delivered
Comparable engagements we have delivered. Client names are withheld; the work is not.
View all case studiesComprehensive Entra Security Review and Ongoing Partnership with a Global Financial Services Group
A global financial services group operating across multiple international markets engaged Modern 42 for an independent security review of its Microsoft Entra environment. What began as a focused assessment has since evolved into a strategic, ongoing partnership.
Data-Driven IAM Discovery and Planning for a Major Healthcare Provider
A large Australian healthcare provider with international operations engaged Modern 42 to conduct a data-driven discovery of its identity landscape and develop a practical implementation plan.
Common questions
What is a workload identity?
How long does the assessment take?
What access does the assessment require?
Do you cover agentic AI systems specifically?
Can this assessment support compliance and audit requirements?
How is Microsoft Entra Agent ID licensed?
What features does Microsoft Entra Agent ID provide?
What are overly permissioned applications and why do they matter?
What are agent identities?
Can this be a one-time report or ongoing?
Let’s talk about your identity challenges
No pitch decks. No pressure. Just a straightforward conversation about where you are, where you need to be, and how we can help you get there.
- Understand your current identity posture
- Identify quick wins and critical gaps
- Get actionable recommendations, no strings attached
Free 30 min discussion
No commitment required
Book a time that works for you. We’ll come prepared with initial observations about your industry and common identity challenges.